
Protecting The Digital Front Door: Cybersecurity Essentials For Customer-Facing Platforms
Customer-facing platforms sit at a difficult intersection of convenience and security. Banking portals, payment systems, account dashboards, mobile apps, and online service platforms must make it easy for legitimate customers to complete transactions while making the same processes difficult for attackers to exploit. A security failure can expose financial information, interrupt transactions, enable account takeover, and damage customer confidence.
Start With Stronger Account Access
Passwords remain a common point of weakness. Customers may reuse credentials across websites, choose predictable passwords, or unknowingly provide login information through phishing attacks. Once credentials have been stolen elsewhere, attackers can automatically test them against other platforms through credential-stuffing attacks.
Multi-factor authentication can create another barrier, particularly for sensitive activities. Authentication requirements can also respond to risk. A login from a familiar device may receive different scrutiny than an attempt from a new device in an unusual location followed immediately by a password change.
Account recovery deserves the same attention. Strong authentication loses much of its value if an attacker can bypass it through a weak password-reset process or easily manipulated support channel.
Limit What a Compromised Account Can Do
Stopping every unauthorized login is unrealistic, which makes post-login controls important. A successful sign-in should not automatically give a user unrestricted access to every action or piece of information associated with an account.
Higher-risk actions can receive additional verification. Changing contact information, adding a new payment destination, modifying security settings, or initiating an unusually large transaction may justify another authentication step.
Financial platforms should also examine authorization behind the interface. A customer changing a number in a URL or modifying an application programming interface request should never gain access to another customer’s records simply because the request reached the server successfully.
Watch Behavior After Authentication
A valid username and password do not prove that the person using an account is the legitimate owner. Monitoring what happens after login can reveal activity that authentication alone misses.
Consider a customer who normally signs in from one device, checks an account balance, and makes a few routine transactions each month. A session that suddenly changes profile information, adds a new recipient, and attempts a large transfer within minutes deserves closer inspection.
Effective monitoring looks for deviations that matter rather than treating every unusual action as an attack. The objective is to identify combinations of behavior that indicate meaningful risk while limiting unnecessary friction for legitimate customers.
Know Where Customer Data Travels
The visible website or application is only one part of a customer-facing platform. Data may move through payment processors, customer relationship management systems, identity providers, analytics tools, support platforms, cloud services, and other integrations.
Each connection creates another place where permissions and data exposure need to be considered. Organizations should know what information each service receives, why it needs that information, how long the data is retained, and what access the integration has to internal systems.
This matters for smaller organizations as much as large financial institutions. Companies evaluating SMB business solutions should consider security requirements alongside functionality, particularly when a third-party service will handle customer credentials, payment details, or other sensitive information.
Protect the APIs Behind the Platform
Modern customer experiences often depend heavily on APIs. Mobile applications, web interfaces, partner systems, and internal services may all exchange information through them.
That makes API security a practical priority rather than a purely technical concern. Authentication and authorization should be enforced on the server side for every sensitive request. Rate limits can reduce certain forms of automated abuse, while input validation helps prevent malformed or malicious requests from reaching downstream systems.
Old APIs deserve attention too. A forgotten endpoint from an earlier version of an application may still be accessible even though customers no longer see it. An interface nobody actively uses can remain a viable entry point if it is still connected to production systems.
Build Logging Around Useful Questions
Collecting logs is easy. Collecting information that helps during an incident requires more thought. Security teams should be able to determine who accessed an account, what device or system was involved, which sensitive actions occurred, and whether permissions or account details changed. Logs should also make it possible to connect related events across different systems.
Retention matters because suspicious behavior may not be discovered immediately. If useful records disappear before an incident is investigated, determining what happened becomes much harder. Alerts should focus on events that warrant attention. Thousands of low-value notifications can hide the handful that indicate an active compromise.
Plan for Failure Before It Happens
Security controls reduce risk, but they cannot guarantee that a platform will never be compromised. Incident preparation determines how quickly an organization can respond when preventive measures fail.
Teams need defined procedures for disabling accounts, revoking active sessions, resetting credentials, isolating affected systems, preserving evidence, and communicating internally. Backups should be tested rather than simply assumed to work.
Customer communication also deserves planning. If an incident affects accounts or transactions, customers need accurate information about what happened, what actions have already been taken, and what they should do next.
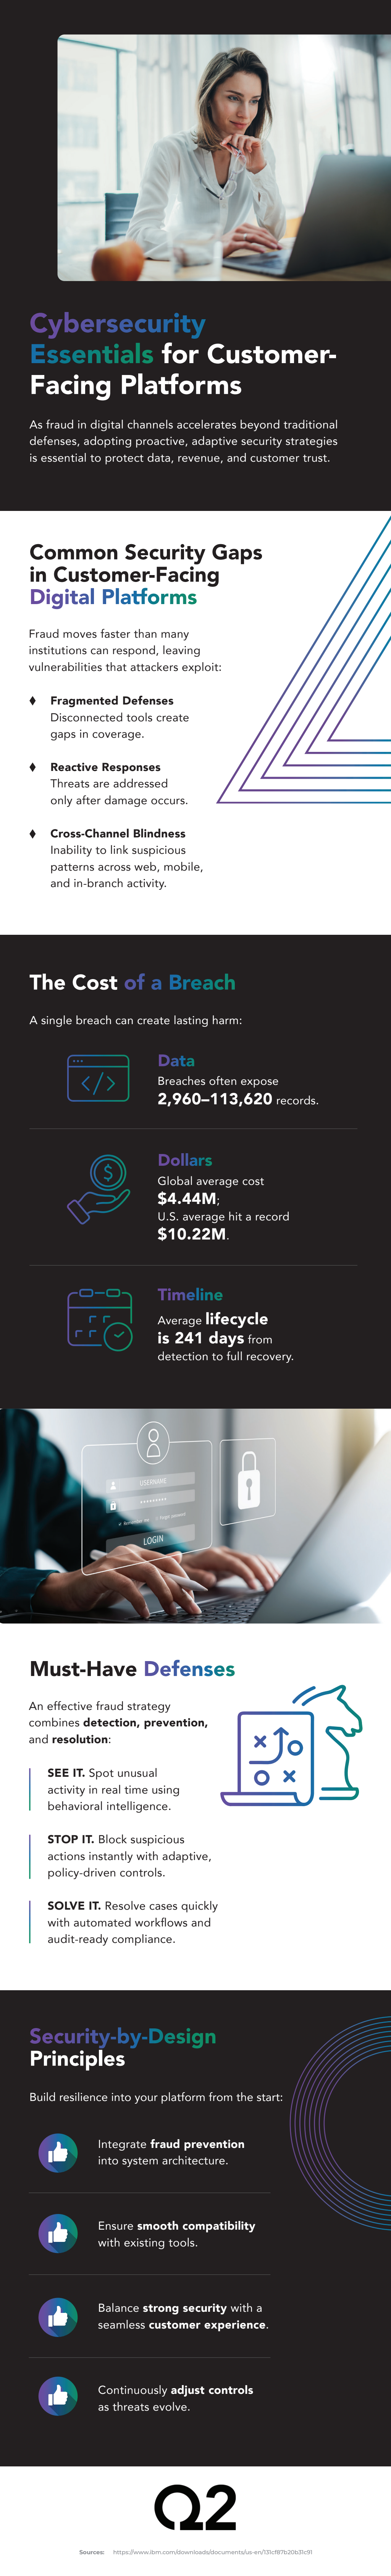
Customer-facing cybersecurity cannot stop at the login screen. Strong authentication matters, but so do authorization, behavioral monitoring, API security, third-party access, useful logging, and incident preparation. Financial organizations that examine the entire customer journey are better positioned to find gaps that individual security products may miss. Look over the infographic below to learn more.